Multi-Tenant SaaS Security Essentials
Multi-tenant SaaS security essentials: isolation on every data path, RBAC, audit logging, secrets hygiene, hostile testing, and habits that keep tenancy trustworthy after launch.
In multi-tenant products, a single missing tenant filter can become a customer-trust incident. Security is not a launch-week checklist—it is a property of how identity, authorization, and data access are modeled on every read, write, job, export, and admin action.
Buyers increasingly ask how you isolate tenants, who can access production data, and what you log when something goes wrong. Strong answers come from architecture and operating discipline, not from a policy PDF added after the first enterprise deal.
Non-negotiable foundations
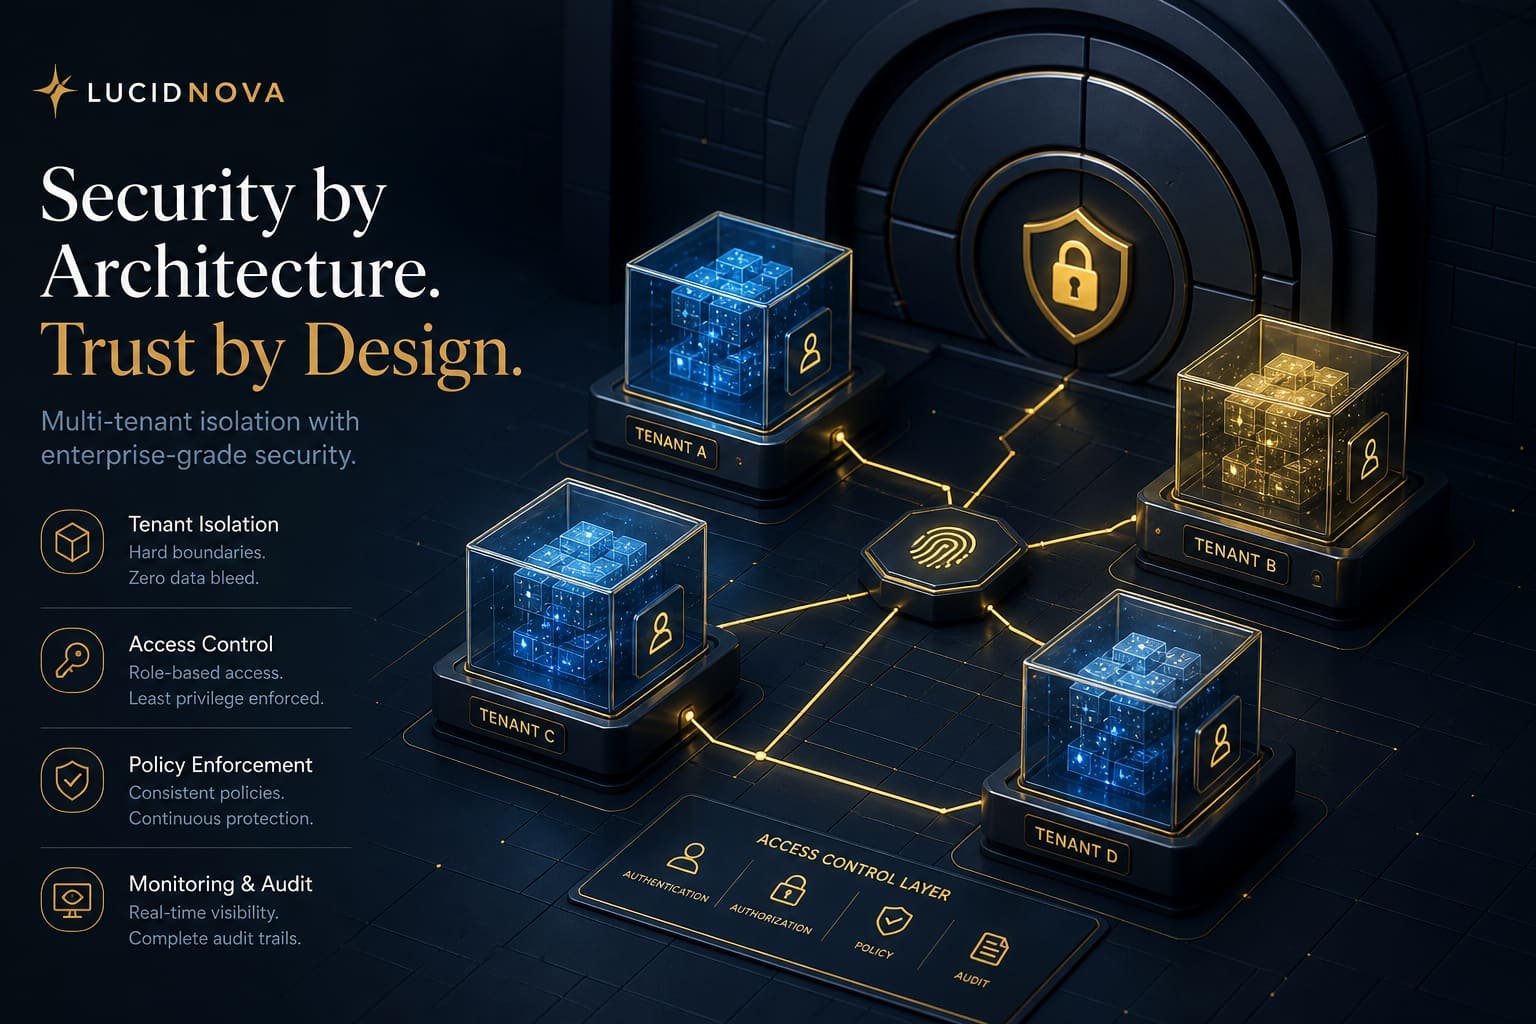
Treat tenant identity as mandatory context, not an optional query parameter. Every persistence layer, cache key, search index document, and message payload should carry tenant scope unless you have a documented, audited exception.
- Tenant identity enforced in application logic and data access layers
- Role-based permissions with least-privilege defaults for customers and staff
- Encrypted secrets, separated environments, and no production credentials in developer machines
- Audit logs for sensitive reads, writes, impersonation, and configuration changes
Isolation models and trade-offs
Shared-schema multi-tenancy is common and can be secure when every path enforces tenant keys and tests prove it. Separate databases per tenant reduce blast radius but increase operational cost. Hybrid approaches—shared app tier with isolated data stores for regulated customers—appear as you move upmarket.
Whatever model you choose, document it for engineering and support. Ambiguity about where tenant boundaries live is how “temporary” admin shortcuts become permanent bypasses.
Where teams get hurt
Most incidents are boring engineering mistakes, not sophisticated attacks. Shared caches without tenant keys, background jobs that iterate “all tenants” without scoping, support consoles that search globally, and export features that accept IDs from the URL without re-checking membership are recurring failure modes.
Another quiet risk is over-privileged service accounts. A worker that can read every row because “it is internal” will eventually be invoked from a path that is not as internal as you assumed.
Operational habits that matter
- Regular access reviews for staff, contractors, and service accounts
- Dependency and patch cadence your team can sustain—not a quarterly wish list
- Named incident ownership with contact paths that work outside business hours
- Automated and manual tests that attempt cross-tenant access and ID tampering
If tenant isolation is only enforced in the UI, it is not isolation.
A practical tenancy checklist
Before the first paying customer, walk tenant identity through every path: HTTP handlers, GraphQL resolvers, RPC calls, queue consumers, cron jobs, analytics pipelines, and backup restores. If any path can omit the tenant key, file a defect and block launch for that feature.
- Admin impersonation is logged, time-bounded, and requires elevated approval
- Exports and reports default to tenant scope; bulk operations need explicit guards
- Support tools cannot browse all customers without a recorded reason
- Webhooks and API keys are tenant-scoped and revocable per customer
Security reviews should include hostile tests: forged tenant IDs, horizontal privilege escalation between users in different orgs, and staff tools used without impersonation audit. Passing a demo walkthrough is not the same as proving isolation under adversarial input.
Build it into v1
Retrofitting tenancy after features ship is expensive and error-prone. Design boundaries early, even when customer count is small. LucidNova treats tenant isolation, auditability, and least privilege as product requirements from the first release—so growth does not force a trust-breaking rewrite.
Contact LucidNova Technologies · hello@lucidnovatech.com · Mumbai, Maharashtra, India